Microsoft SharePoint Remote Code Execution Vulnerability CVE-2026-65660
Microsoft patched CVE-2026-65660, a SharePoint remote code execution issue rated CVSS 3.1 8.8, with a public proof of concept and no in-the-wild use reported in the notice. On-premises Subscription Edition, 2019, and 2016 builds below the listed fixed versions should be updated.
Overview
QiAnXin CERT reported a Microsoft SharePoint remote code execution vulnerability tracked as CVE-2026-65660 and QVD-2026-51137. Microsoft’s public date for the issue is 2026-08-11. QiAnXin rated it high, with a CVSS 3.1 score of 8.8. The threat type is code execution. QiAnXin assessed exploitation likelihood as high.
A proof of concept, exploit code, and technical details are public. In-the-wild exploitation had not been observed at the time of the notice. QiAnXin estimated the impact scale at the 100,000-asset level.
Product
Microsoft SharePoint Server is an enterprise collaboration and content platform from Microsoft. It is used for document management, team collaboration, intranet portals, workflow, and business intelligence. SharePoint Server Subscription Edition is the subscription, on-premises release.
Impact
On affected SharePoint Server deployments, the vulnerability can lead to remote code execution. Persistence after code execution is described as possible. Use may be unauthenticated if the target web application has anonymous access enabled. If anonymous access is off, a valid low-privilege SharePoint account is required.
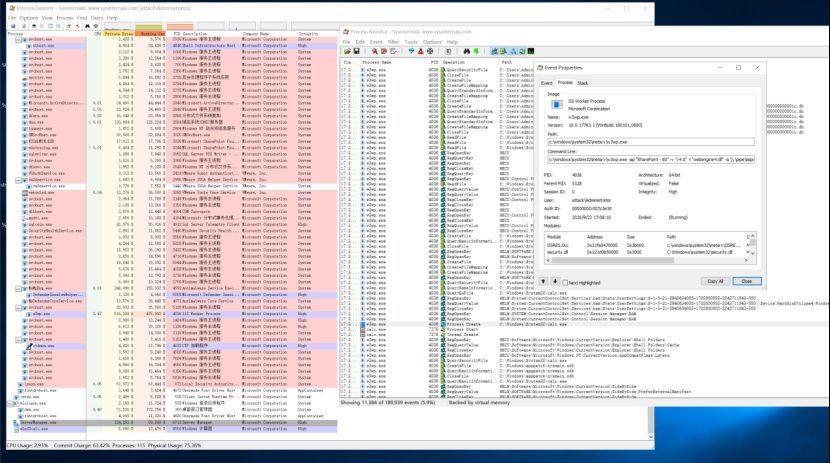
QiAnXin CERT said it reproduced the issue.
Affected versions
The notice lists these ranges:
- Microsoft SharePoint Server Subscription Edition from 16.0.0 up to, but not including, 16.0.19725.20522
- Microsoft SharePoint Server 2019 from 16.0.0 up to, but not including, 16.0.10417.20198
- Microsoft SharePoint Enterprise Server 2016 from 16.0.0 up to, but not including, 16.0.5565.1001
No other components are listed as affected.
Observed exposure
QiAnXin Eagle Map listed 5,209 associated at-risk assets in China and 285 associated IPs.
Globally it listed 67,103 associated at-risk assets and 7,912 associated IPs.
Patching
Microsoft has released security updates. Move to these versions or later:
- Microsoft SharePoint Server Subscription Edition 16.0.19725.20522
- Microsoft SharePoint Server 2019 16.0.10417.20198
- Microsoft SharePoint Enterprise Server 2016 16.0.5565.1001
Microsoft security update guide: https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-65660
QiAnXin advised customers to inventory on-premises SharePoint Server systems and apply the vendor patch promptly, given the public proof of concept and the size of the exposed asset set.
References
1. https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-65660 2. https://blog.viettelcybersecurity.com/sharepoint_cve-2026-65660/