ShinyHunters Claims Theft of All FBI Employee and Applicant Data
ShinyHunters told 404 Media it had stolen records on all FBI employees and applicants, including names, home addresses, phone numbers, and spouse information. Reporters checked a 5,000-record sample against open-source tools, and the group also defaced the FBI recruiting site while claiming 2 to 3 TB from AWS GovCloud.
Anquanneican reported on 23 September 2026 that the group ShinyHunters claimed it had broken into multiple Federal Bureau of Investigation systems and taken data on all FBI employees and applicants.
The group told 404 Media the haul included FBI agent names, home addresses, telephone numbers, and spouse information. 404 Media described possible national security and counterintelligence effects if the records spread, including use by foreign services and by criminals. Members of the same criminal ecosystem had previously used stolen telephone records to track, threaten, and harass FBI agents who were investigating them.
Sample records checked by reporters
ShinyHunters told 404 Media it had hacked the FBI and held data on all FBI employees and applicants.
The group supplied a sample said to cover personal information on 5,000 FBI employees, including purported addresses, telephone numbers, dates of birth, and, for some people, spouse information.
404 Media entered some of the sample telephone numbers into the open-source intelligence service OSINT Industries and found the numbers matched people with the names listed in the file. The outlet also searched some records in Darkside, a leaked-data lookup tool from cybersecurity firm District 4. Some of those numbers were associated with U.S. Department of Justice staff.
Anquanneican said the released officer sample had been checked and found to match real people, and that the FBI said it was investigating.
Recruiting site defacement
ShinyHunters also defaced the FBI recruiting website. The altered page stated that the site had been taken over by ShinyHunters, in the style of seizure banners used by the FBI and other law enforcement agencies.
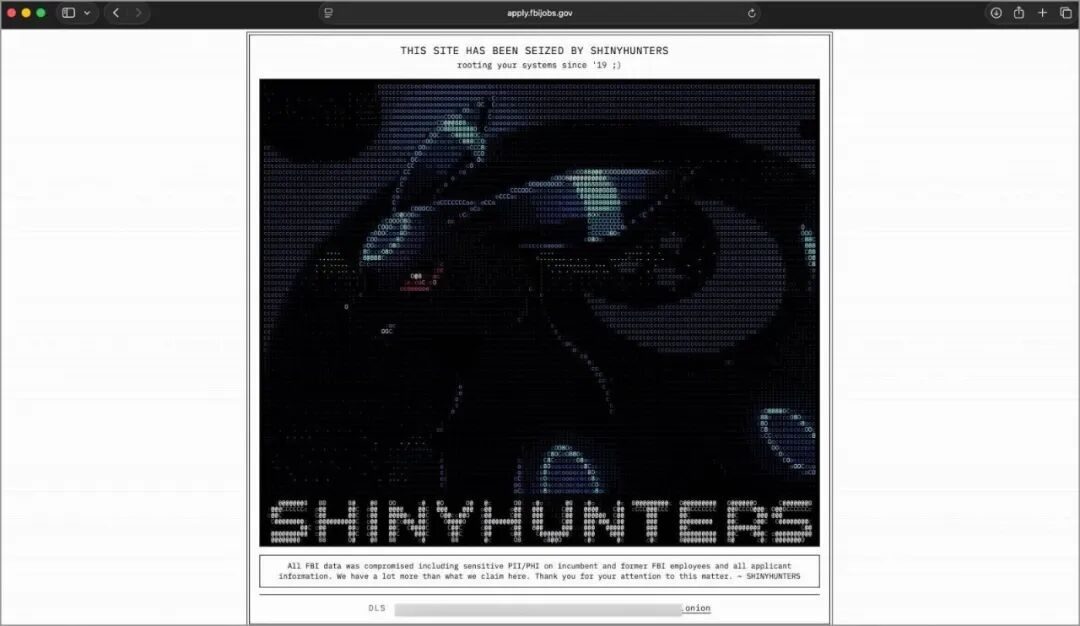
The group carried out the site attack on Monday evening. At the time of the 404 Media report, the FBI recruiting site said Apply.fbijobs.gov and the special-agent application portal were unavailable.
The defaced page claimed that all FBI data had been leaked, including personally identifiable information and protected health information (PII/PHI) of current and former FBI employees, plus all applicant information, and that the group held more data than the banner described. The statement closed with a line styled after President Trump's posts on Truth Social thanking readers for their attention to the matter.
404 Media said the FBI had not immediately responded to a request for comment.
Claimed volume and systems
ShinyHunters said it used a zero-day vulnerability in Oracle PeopleSoft and then reached AWS GovCloud servers. The group said the stolen volume was 2 to 3 terabytes.
The group typically compromises a target and then demands payment under threat of further disclosure. Asked whether it would extort the FBI, ShinyHunters said it would not call the next steps extortion and preferred the word coercion, and that the operation was not for economic gain.
404 Media's report is at https://www.404media.co/we-hacked-the-fbi-hackers-say-they-have-data-on-all-fbi-employees/.